Knowledge Center
Understand. Decide. Implement.
A structured entry point for turning cybersecurity requirements into decisions, documents, measures and evidence.
- Official sources, not isolated interpretationsWe identify the law, regulation or guidance supporting each answer.
- Reviewed and dated contentWe show when information was checked so that its context remains clear.
- Clarity for decision-makingWe explain complex subjects in direct language without losing technical rigour.
- From obligation to evidenceWe connect requirements to the necessary actions, documents, measures and proof.
- Pathways, not isolated pagesWe connect concepts, obligations, questions, resources and next steps to preserve the full context.
Knowledge map
Choose the subject. We organize the pathway.
Each pathway combines context, explanation, implementation and sources to help people and organizations move forward securely.
Framework
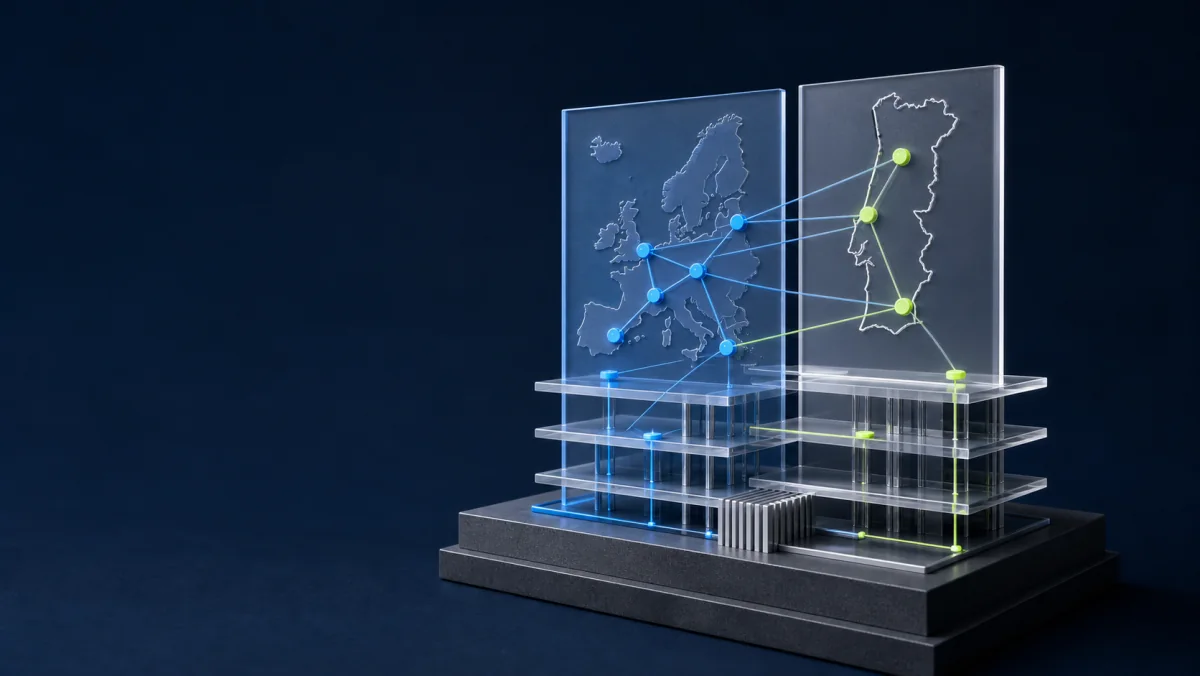
RJCS and NIS2
Scope, entities, responsibilities, obligations and the relationship between the European and Portuguese frameworks.
Open content →
Legislation
Decree-Law No. 125/2025
A structured reading of the legislation, including obligations, deadlines, responsibilities, questions and practical cases.
Open content →
Regulation
Regulation No. 756/2026
Measures, evidence, risk, qualification and guidance for implementation.
Open content →
Pathway
MyCiber
Registration, self-identification, qualification, Cybersecurity Officer, Permanent Point of Contact, evidence, guides and FAQ.
Open content →
Governance and leadership
vCISO: external cybersecurity leadership
The vCISO professional role, its mandate and how it differs from CISOaaS and a formally appointed cybersecurity officer.
Open content →
Data protection
Data Protection Officer
Role, requirement, independence, internal and external models, appointment and CNPD notification.
Open content →
Managed cybersecurity
Cybersecurity as a Service: understanding CSaaS
How to organize governance, protection, monitoring and response as a managed service without losing accountability.
Open content →
Technology lifecycle
Technology as a Service: understanding TaaS
How to structure devices, software, cloud, support and renewal in a managed technology model.
Open content →
Network operations
NOCaaS: Network Operations Center as a Service
Availability, performance, alerts and escalation: what belongs to a NOC and where security begins.
Open content →
Integrated operations
NSOC: integrating network and security operations
How to connect NOC and SOC through a shared operational view without mixing objectives, expertise or responsibilities.
Open content →
Operations
Implementation Center
How to apply measures, produce documents, collect evidence and keep the system operating.
Open content →
Reference
Glossary and FAQ
Concepts, direct answers and links to more detailed content.
Open content →Quick pathways
Start with the need, not the legislation.
Operational reading
Explore the steps that require a decision.
Implementation
Do you understand the requirement?
The next step is to turn the obligation into a plan, measures and verifiable evidence.