
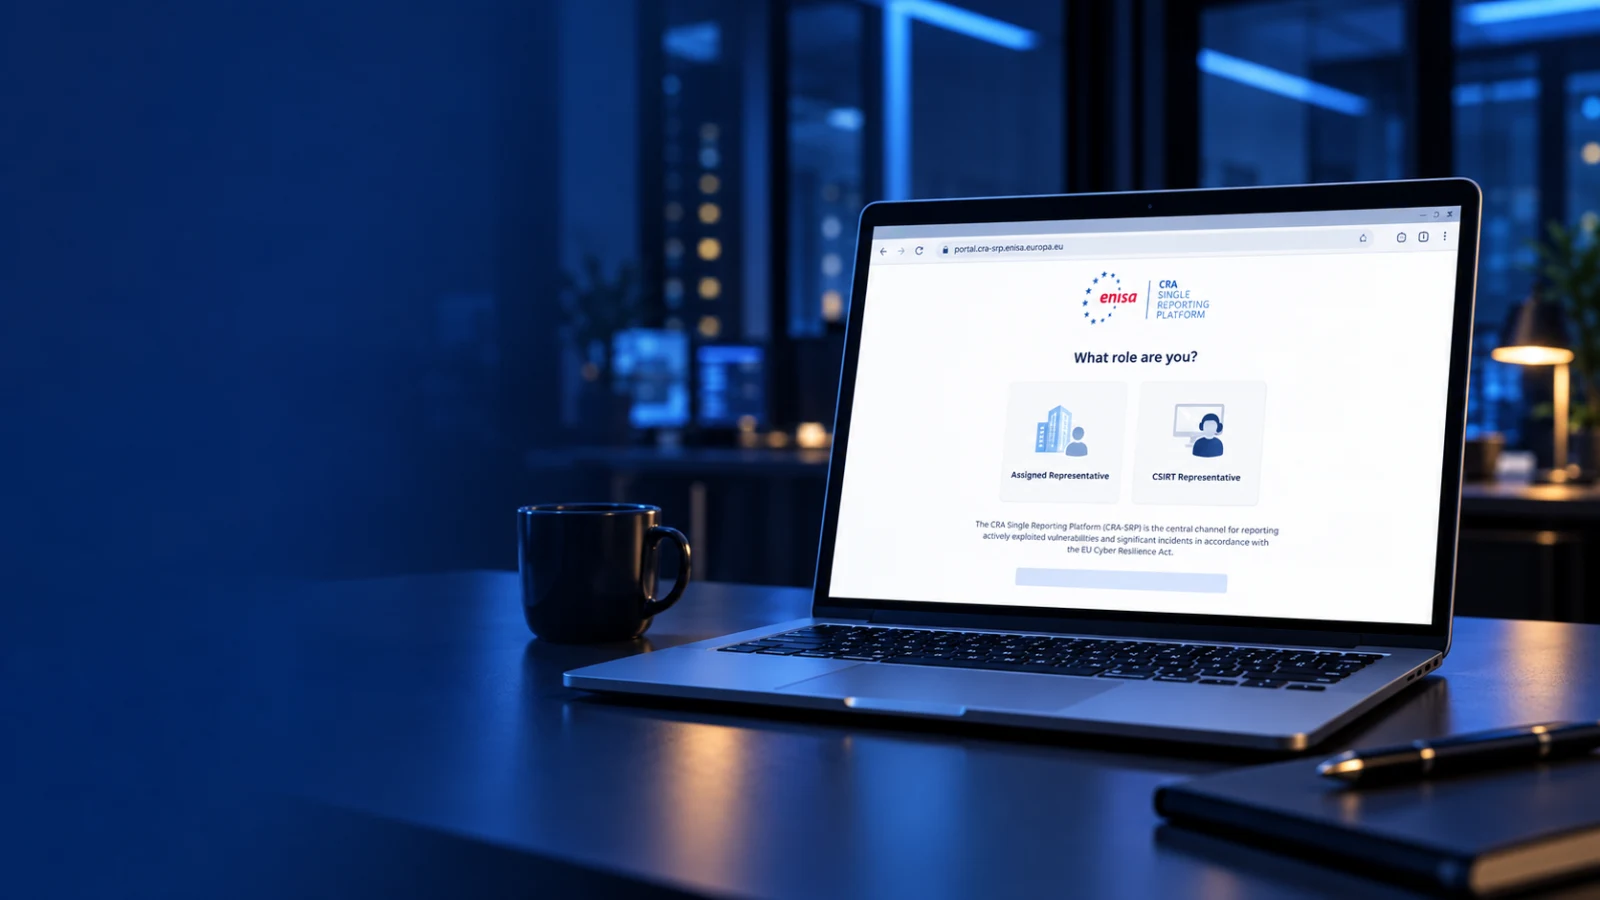
A single reporting point, not an automatic response
ENISA has launched the Single Reporting Platform (SRP) required by the Cyber Resilience Act. Since September 11, 2026, manufacturers of products with digital elements and open-source software stewards within scope can use it to report actively exploited vulnerabilities and severe incidents affecting product security.
A notification is submitted once and securely routed to the coordinator CSIRT, other relevant CSIRTs, and ENISA. Centralized reporting reduces duplication, but it does not replace internal detection, technical assessment, decision-making, or fact collection.
Two dates must be kept distinct: reporting obligations have applied since September 11, 2026; the CRA’s other main requirements generally apply from December 11, 2027.
The clock starts when awareness exists
According to the European Commission, reporting begins with an early warning within 24 hours after the manufacturer becomes aware of the situation. A complete notification follows within 72 hours.
For an actively exploited vulnerability, the final report is due no later than 14 days after a corrective or mitigating measure becomes available. For a severe incident, it is due within one month after the 72-hour notification.
These deadlines make it essential to record when awareness arose, who classified the situation, which products and versions are affected, what exploitation or impact was observed, and which measures were taken.
- Within 24 hours: early warning using the information available and identifying potentially affected Member States.
- Within 72 hours: fuller notification including assessment, severity, impact, and available indicators of compromise.
- Final report: cause, impact, mitigation or correction, and information relevant to closure.
Access through assigned representatives
The portal distinguishes organization representatives from CSIRT representatives. An Assigned Representative submits CRA notifications on behalf of a manufacturer or open-source software steward.
ENISA provides for one Primary Assigned Representative and up to 20 Secondary Assigned Representatives per entity. Access uses EU Login with multifactor authentication. This distribution supports continuity, but mandates, substitutes, and access reviews should be documented.
At initial launch, the platform uses an English-language web interface and does not yet offer a public submission API.
What to prepare before reporting is needed
A 24-hour window is incompatible with searching for owners, products, and evidence only after an incident has been confirmed. Preparation should connect product security, development, operations, legal support, communications, and management.
Cyberprotech recommends a short, documented exercise covering the full pathway from detection to submission. The aim is not to pre-fill every answer, but to know where reliable information can be obtained when the clock starts.
- Confirm potentially in-scope products, versions, third-party components, and legal entities.
- Appoint the primary representative and substitutes, enable EU Login MFA, and review access regularly.
- Define internal criteria for actively exploited vulnerabilities and severe incidents, with escalation outside normal hours.
- Prepare a minimum data set: product, versions, affected countries, timeline, impact, indicators, mitigation, and contacts.
- Record time of awareness, decisions, technical sources, limitations, and changes between reporting stages.
- Identify the coordinator CSIRT and test coordination between technical teams, management, and compliance roles.
- Exercise platform unavailability and retain evidence of attempts; urgent contact with a CSIRT does not remove the later SRP submission requirement.
Confidentiality does not remove the need for minimization
ENISA states that the platform is designed to protect notification confidentiality. Organizations should still submit relevant, validated data and avoid personal or operational information that is unnecessary for the reporting purpose.
Process quality depends on traceability across detection, analysis, decision, correction, and communication. A central form cannot fix incomplete inventories, unclear responsibilities, or missing post-market product monitoring.
Turning an obligation into operational capability
The SRP simplifies the European entry point. The essential work remains inside the organization: recognize the situation quickly, gather facts, make accountable decisions, and track remediation.
Cyberprotech can help prepare the workflow, responsibilities, minimum data, exercises, and evidence by connecting product security, incident response, and compliance. This article is informational and does not replace the CRA, official guidance, or assessment of the specific applicable framework.